
Cyber Digest

CERT-FR, CNIL and EUR-Lex publications, summarised by AI

Cyber Digest aggregates the last three months of publications from official sources and extracts the essentials with AI: a summary, the CVEs with their severity, the products concerned and what to do. Reading is free and requires no account, and email alerts can be filtered on the products in your estate.

Nothing to install, no data to provide. The time of the last update is shown at the top of the page. The feed is in French.

Extract from the feed, Cybersecurity tab

15 October 2026

CERT-FRVulnérabilité15 Oct 2026

Vulnérabilités F5 - Exécution de code à distance

Multiples vulnérabilités dans les produits F5 permettant exécution de code à distance, atteinte à la confidentialité et intégrité des données, avec risque d'exploitation.

Produits concernés : F5 - produits non spécifiés

Conduite à tenir : Vérifier l'exposition du SI à ces produits puis contacter F5 pour correctifs ou contournements.

CERT-FRVulnérabilité15 Oct 2026

Vulnérabilités XSS et contournement dans Moodle

Failles XSS et contournement de politique de sécurité dans Moodle, risque d'injection de code à distance, exploitation non mentionnée.

Produits concernés : Moodle (versions non spécifiées)

Conduite à tenir : Vérifier l'exposition du SI à Moodle puis planifier la mise à jour vers une version corrigée.

CERT-FRVulnérabilité15 Oct 2026

Vulnérabilité dans PostgreSQL psqlODBC

Vulnérabilité permettant un déni de service à distance, sans information sur exploitation active.

Produits concernés : PostgreSQL psqlODBC

Conduite à tenir : Vérifier l'exposition du SI à ce produit puis planifier une mise à jour ou un correctif.

The three most recent advisories at the site’s last update, in French. The live feed reloads every time the page is opened.

Scope

Three sources, one feed

CERT-FR with its four types of publications (alerts, security advisories, recommendations, news bulletins), the CNIL and EUR-Lex: six feeds, each on its own site, at its own pace, in a raw format. Every advisory has to be opened to know whether a product in the estate is concerned, and that sorting falls to the CISO or the DPO.

Cyber Digest brings these feeds together on one page, in two tabs, cybersecurity on one side, legal and compliance on the other, over the last three months. Every entry keeps the link to the original publication, which gives a basis for the monitoring process expected by ISO 27001 (control A.5.7).

The scope is limited to these three sources, in French. Summaries are generated automatically; the official publication remains the only authoritative reference. For an evidential archive or a reconciliation with your inventory, other tools are needed.
CERT-FR

Alerts, security advisories, recommendations (hardening guides) and news bulletins, each with its own tag. Every entry links back to the original publication on cert.ssi.gouv.fr.

CNIL

Publications of the French data protection authority, in the legal and compliance tab.

EUR-Lex

European Union texts and regulatory changes, in the same tab.

AI summary

AI extracts the essentials of each publication

  • A summary in French, generated by AI, to decide at a glance whether the topic concerns you.
  • For CERT-FR alerts, the CVE identifiers with a colour badge by CVSS severity (critical, high, medium, low) and the score in a tooltip.
  • The products concerned: vendor, product and versions targeted, when the source specifies them.
  • What to do: check the exposure of your systems, plan an update, apply a patch, contact the vendor.

Sorting

Sorted by tab, period and keyword

Two tabs, cybersecurity on one side, legal and compliance on the other. The period ranges from today to the last three months, and the search covers titles, summaries, CVEs and products: a vendor name is enough to find what concerns you.

Reliability

A public page, up to date and sourced

The time of the last update is shown at the top of the page, and every entry links to the official publication. AI-generated summaries are flagged as such by the “Augmentée par l’IA” (Augmented by AI) badge. No account to create, no data to provide to read the feed.

Notifications

Three email subscriptions, alerts filtered on your estate

  • CERT-FR alerts as soon as they are published, the daily digest of every security advisory from the day before, and the weekly legal newsletter (CNIL and EUR-Lex). The three are ticked separately and are off by default.
  • When you switch alerts on, you list the products in your estate, one word per product, no version number. You only receive the alerts that concern them. With no product listed, everything is sent.
  • Only the email address is collected, preferably a team list or alias, plus the list of product names if you give it. Nothing personal, nothing about your architecture.

Emails

What you receive

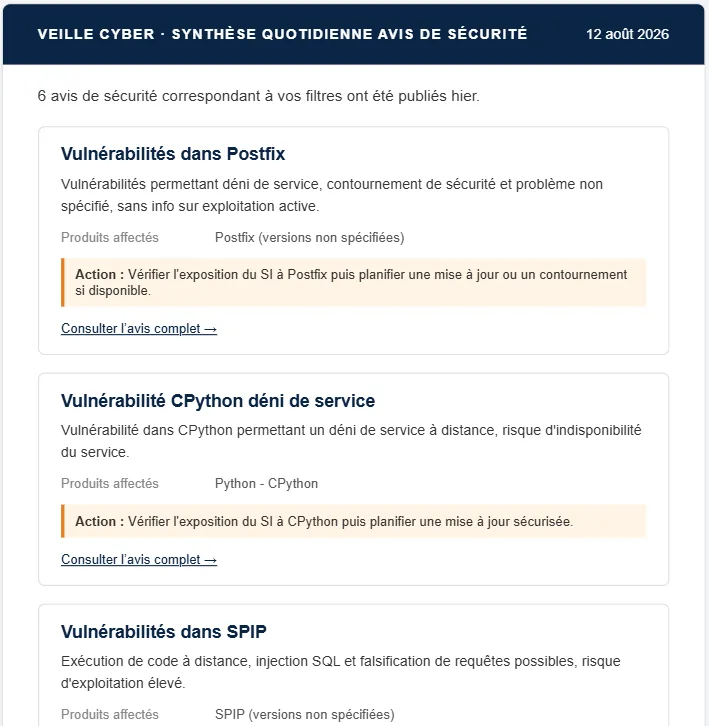
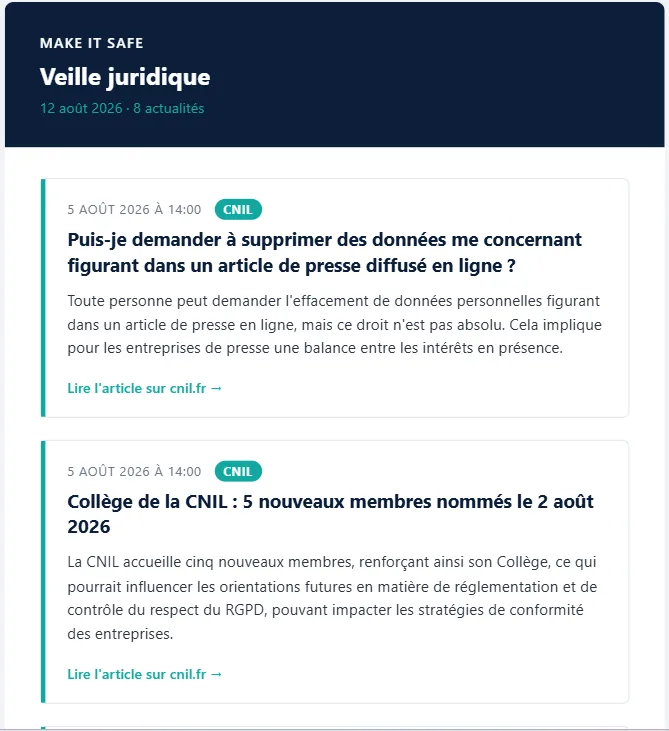
The daily digest lists the security advisories published the day before, with the affected products and the recommended action for each. The legal newsletter covers the week’s CNIL and EUR-Lex publications, summarised, with a link to the original article. Emails come from a single sender, to be allowed through your spam filter. They are in French.

A daily digest email: the security advisories published the day before, with affected products and recommended action
The daily digest.
A legal watch email: the week’s CNIL publications, summarised, with a link to the original article
The legal newsletter.

The Make IT Safe suite

The GRC platform and the dedicated solutions

Open today’s feed

Reading requires no account. Email notifications are switched on from the page itself.