
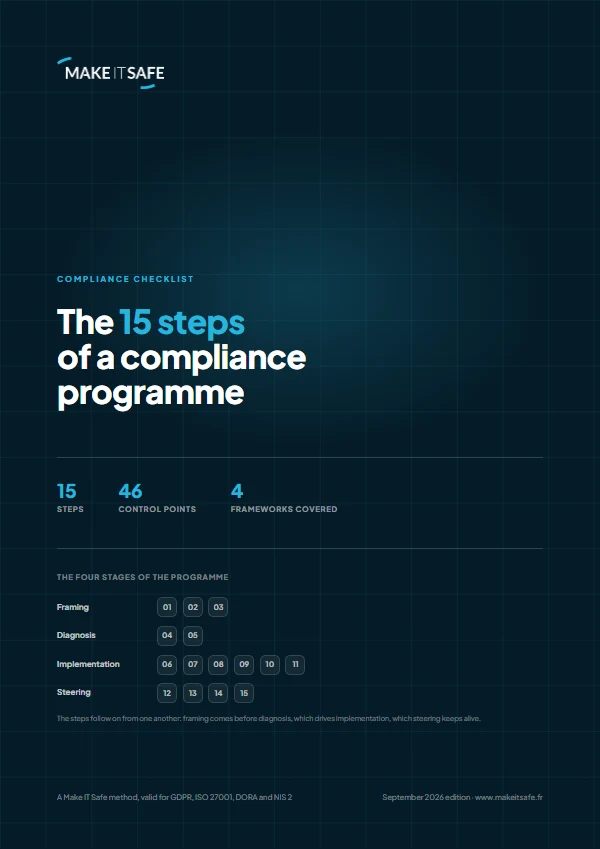
With cyberattacks multiplying and regulations tightening, companies of every size face a major challenge: securing their systems while remaining compliant with the standards in force. Whether you are a Chief Information Security Officer (CISO), a DPO or even a company executive, it is essential to understand how to manage cyber risks effectively and meet regulatory requirements.
Risk management in cybersecurity is not only about protecting data and systems, but also about adopting a proactive approach to identify vulnerabilities, put protective actions in place and guarantee that the company remains compliant with the legal and normative frameworks in force, such as the GDPR, the NIS 2 Directive or the ISO 27001 standard.
In this article, we will explore in depth the various aspects of risk management and compliance in cybersecurity, as well as the best practices for achieving them. We will also look at the tools that make this process easier, in particular the SaaS solutions that centralise and automate security and compliance work.
Understanding what is at stake in cybersecurity and risk management
Cybersecurity is today one of companies’ strategic priorities. The development of digital technologies has allowed organisations to optimise their processes, but it has also increased their exposure to cyber threats. These threats can have dramatic consequences: financial losses, damage to reputation, data theft or regulatory sanctions.
Why cybersecurity is crucial for companies
The constantly evolving digital landscape makes companies increasingly vulnerable to cyberattacks. These attacks can take different forms: phishing, ransomware, theft of sensitive data, and many others. Faced with these risks, it is imperative for companies to adopt a robust cybersecurity strategy.
A successful attack can not only disrupt day-to-day operations, but also lead to a loss of trust from customers and partners. In addition, the legal sanctions that result from failing to comply with regulations can prove costly, both financially and in terms of reputation. Cybersecurity thus becomes an essential component in ensuring the long-term future of the company.
What is cyber risk management?
Cyber risk management consists of identifying, assessing and mitigating the threats that weigh on the company’s information systems. It aims to anticipate potential attack scenarios, put prevention measures in place and define suitable action plans in the event of an incident.
Here are the main steps of cyber risk management:
- Risk identification: analyse the various vulnerabilities present in the IT systems, as well as external threats.
- Risk assessment: prioritise risks according to their likelihood of occurrence and their potential impact.
- Implementation of corrective actions: deploy technical and organisational solutions to reduce the risks identified.
- Continuous monitoring and reassessment: keep constant track of threats and adapt actions according to technological and regulatory developments.

Compliance: a pillar of modern cybersecurity
Risk management in cybersecurity is not limited to protecting systems and data. It also includes compliance with the various regulations and standards in force. Companies must not only defend themselves against cyber threats, but also guarantee that they comply with the laws and normative frameworks imposed by governments and regulatory bodies. Non-compliance can lead to financial sanctions, lost contracts and damage to reputation.
The main regulations to know
For companies, there are several regulatory and normative frameworks that it is essential to comply with in order to ensure optimal security and effective risk management. Among the most important are:
- GDPR (General Data Protection Regulation): this European Union regulation requires companies to protect the personal data of European citizens. It places the emphasis on transparency, user consent and data security.
- ISO 27001: this international standard sets out a framework for implementing an information security management system (ISMS). It is widely adopted to manage risks and guarantee the confidentiality, integrity and availability of information.
- NIS 2 (Directive on the security of network and information systems): this European directive requires critical sectors (energy, transport, finance, health, etc.) to ensure a high level of cybersecurity.
- DORA (Digital Operational Resilience Act): this framework regulates the digital operational resilience of financial institutions, requiring them to strengthen their systems against cyber threats.
Each company must assess the regulations that apply to its sector and put appropriate measures in place to meet them. Adopting a compliance framework not only reduces the risk of sanctions, but also optimises the management of cyber risks.
The importance of compliance for risk management
Regulatory compliance is more than a simple legal obligation. It plays a central role in the company’s risk management strategy. Indeed, regulations often impose requirements in terms of cybersecurity, such as the introduction of technical and organisational measures, the training of staff, and the continuous monitoring of systems.
Companies that meet these requirements reduce their exposure to cyber threats while at the same time making sure that they are in a position to respond to incidents in an effective manner. Here is why compliance is an essential asset for risk management:
- Risk reduction: complying with standards and regulations guarantees that robust cybersecurity practices are put in place, which reduces the vulnerabilities.
- Improved resilience: by complying with regulatory frameworks, companies adopt resilience strategies that allow them to cope better with incidents.
- Stronger stakeholder trust: customers, partners and regulators have greater confidence in a company that complies with the legal requirements and that protects information.
Best practices for managing risks and ensuring compliance
Cyber risk management and compliance with regulations are not one-off tasks, but rather continuous processes that must be integrated into the overall strategy of the company. In order to guarantee effective protection against threats and to comply with legal requirements, it is essential to adopt best practices in risk management and security. These practices must be adaptable and scalable, and must be regularly updated in line with new threats and with regulatory developments.
Analysing and identifying risks
The first step in any risk management strategy is a rigorous risk analysis. This makes it possible to identify potential vulnerabilities and assess the threats facing the company. A poor risk assessment can lead to serious incidents, hence the importance of putting a structured process in place.
Here are the main steps in analysing and identifying risks:
- Mapping critical assets: identifying the company’s critical assets is a fundamental step. These may be information systems, sensitive data, operational processes or key human resources. This step makes it possible to know precisely what needs to be protected as a priority. An asset management system can be used to automate and centralise this identification.
- Identifying vulnerabilities: once the critical assets have been identified, the next step is to assess the associated vulnerabilities. These include software flaws, human errors, outdated processes and inadequate system configurations. Vulnerability scanning tools make it possible to carry out this assessment in real time.
- Assessing threats: a company can face a multitude of threats. It is therefore essential to draw up an overview of the risks to which it is exposed, such as external cyberattacks (malware, ransomware, phishing) or internal threats (data leaks, human error). This assessment must take into account not only current threats, but also those that could emerge in the future.
- Assessing the impact and likelihood of risks: once the threats have been identified, it is crucial to assess their potential impact on the organisation, whether in financial terms, in terms of reputation or in terms of business continuity. Each risk must be scored according to its likelihood of occurrence and its level of severity. The highest risks are those that require immediate attention and specific prevention measures.
- Drawing up a risk management plan: after identifying and assessing the risks, the company must draw up a risk management plan that includes prevention, mitigation and incident response strategies. This plan must be clear, detailed and adaptable to changes in the company’s context.

Implementing effective security controls
Good risk management is not limited to analysis. It is imperative to put in place security controls suited to the threats identified. These controls must cover several aspects: technical, organisational and human. The objective is to reduce the likelihood of incidents and mitigate their impact in the event of an attack.
Here are a few examples of security controls:
- Securing access and identity management (IAM): one of the most critical aspects of security is controlling who has access to what. Companies must put in place identity and access management policies that include strict permissions and strong authentication (such as multi-factor authentication). This limits the risk of unauthorised access to sensitive data or critical systems.
- Data encryption: encryption is an indispensable measure for protecting sensitive data, both at rest and in transit. Using robust encryption algorithms and security certificates ensures that, even if a compromise occurs, the data will remain unreadable to attackers.
- Updating and patching systems: many attacks exploit security flaws in software or systems that are not up to date. It is therefore crucial to put in place a rigorous process for updating systems and applying security fixes (patch management).
- Real-time detection and monitoring: putting threat detection and monitoring solutions in place, such as intrusion detection systems (IDS), makes it possible to identify suspicious behaviour quickly. This proactive monitoring makes it possible to react faster to incidents and limit the damage. In parallel, SIEM (Security Information and Event Management) solutions collect and analyse system data to detect anomalies.
- Network segmentation: separating the network into different zones (for example, a public zone for services accessible over the internet and a private zone for sensitive data) makes it possible to limit the impact of an intrusion. In the event of an incident in one part of the network, this prevents attackers from moving freely to other critical systems.
- Employee awareness and training: people are often the weakest link in cybersecurity. Companies must regularly train their employees in good security practices (for example, recognising phishing attempts, using strong passwords) and in the procedures to follow if an incident is suspected.
Ensuring continuous compliance
Compliance is not limited to ticking boxes during an audit. It is a continuous process that must be integrated into the company’s risk management strategy. It evolves according to new threats, regulatory requirements and technological developments.
Here are some practices for ensuring continuous compliance:
- Regulatory watch and policy updates: regulations change regularly, and it is essential to keep an active watch in order to remain compliant with new requirements. Monitoring and analysis tools make it possible to anticipate regulatory changes and quickly adapt internal processes.
- Internal and external audits: audits are an effective way of making sure that security and compliance policies are properly applied. Regular internal audits, as well as external audits carried out by third parties, make it possible to identify gaps in risk and compliance management and to make the necessary corrections.
- Automating compliance processes: using software tools, in particular dedicated SaaS solutions, makes it possible to automate compliance-related tasks (document management, control tracking, report generation, etc.). This not only reduces human error, but also saves time and improves the overall efficiency of processes.
- Reporting and documentation: it is crucial to document every step of the risk management and compliance process. This guarantees transparency towards regulators and auditors, but also towards customers and partners. Clear and precise documentation is also a valuable tool in the event of a dispute or investigation.
- Compliance culture: compliance should not be seen as a constraint, but as an integral part of the company culture. It is important that all employees, at every level of the organisation, are aware of the regulatory requirements and of the risks incurred in the event of non-compliance. This involves regular training, awareness-raising and clear communication on the importance of security and compliance.
Tools that make risk management and compliance easier
Faced with the growing complexity of cyber threats and of regulatory requirements, companies need effective tools for steering the management of risks and for ensuring continuous compliance. These tools, often in the form of SaaS solutions, offer numerous features that make it possible to centralise, automate and optimise the processes related to security and compliance. They represent a precious saving of time and resources, while also offering better visibility over security performance.
Why use a SaaS solution for risk management and compliance?
SaaS (Software as a Service) solutions have become unavoidable for companies that wish to improve their risk management and their compliance. Unlike on-premises solutions, they offer increased flexibility, accessibility and scalability. Here are a few reasons why a dedicated SaaS solution is particularly advantageous in this area:
- Access at any time and from anywhere: with a SaaS solution, teams are able to access their dashboards and their security management tools from any location, which is crucial for companies that have teams spread across several countries or regions. This also makes it possible to coordinate actions more easily with external stakeholders, such as security consultants or auditors.
- Regular updates and automatic compliance: regulations are constantly changing, and keeping up with the changes can be a complex and time-consuming task. A SaaS solution provides regular updates to incorporate new regulatory requirements, which allows companies to remain compliant without having to invest on a constant basis in manual updates or in costly adaptations of their systems.
- Process automation: automating tasks such as risk assessment, compliance report generation or incident tracking considerably reduces human error while ensuring greater responsiveness to threats or legislative changes. Automation also makes it possible to generate real-time alerts when gaps or risks are identified, ensuring fast and informed decision-making.
- Real-time analysis of security performance: SaaS solutions offer real-time monitoring and reporting features that allow CISOs and security teams to have an overall view of the state of the company’s security. This includes detailed reports on risks, on corrective actions, and on compliance with standards.

The key features of a SaaS solution
A SaaS solution for risk management and compliance generally offers a set of features designed to cover the entire risk management cycle and ensure continuous compliance. Here are the main features found in these solutions:
- Analysis of third parties and the ecosystem: a SaaS solution makes it possible to assess the risks related to third parties (suppliers, subcontractors, partners). This includes regular assessments of the security levels and compliance practices of these actors, to make sure that they do not represent a vulnerable entry point into the company’s system.
- Security audit and ISMS: a regular security audit is essential to assess the company’s security posture. The SaaS solution can automate this audit and help to set up an Information Security Management System (ISMS) compliant with standards such as ISO 27001. This includes document management, and the tracking of gaps and action plans.
- Risk management and action tracking: risk management is at the heart of any SaaS cybersecurity solution. It makes it possible to identify potential risks, assess them according to their impact and likelihood, and track the progress of the mitigation measures implemented. A dynamic dashboard makes it possible to follow the state of risk management within the organisation in real time.
- Integrating security into projects (ISP): to guarantee that the company’s projects (deployment of new systems, launch of applications, etc.) comply with security requirements, SaaS solutions make it possible to integrate security processes from the very start of projects. This makes it possible to avoid flaws and to comply with security standards throughout the project life cycle.
- Steering cybersecurity at group level: for companies operating internationally or across multiple sites, it is essential to be able to steer cybersecurity centrally, while taking local specificities into account. A SaaS solution makes it possible to coordinate security actions across all the group’s entities, guaranteeing consistent practices and alignment with the company’s overall objectives.
- Implementing and tracking action plans: good risk management includes putting corrective action plans in place to remedy the vulnerabilities identified. A SaaS solution makes it possible to track the progress of these actions and to generate detailed reports on the effectiveness of the measures taken.
- Making it easier to produce the Supplier Security Assurance Plan (SSA): the SSA is the contractual document in which a provider describes the security measures it applies on behalf of its client, and commits to maintaining them. A SaaS solution makes it possible to track its collection, its updates and its coverage of the requirements, while making coordination between the teams involved easier.
- Collaboration and communication around security projects: a SaaS solution makes collaboration easier between security teams, IT departments and the other stakeholders (CISO, DPO, senior management). It offers built-in communication tools, such as discussion spaces, real-time notifications and shared reports.
The specific benefits for CISOs and DPOs
CISO and DPO profiles, responsible for security and compliance within their organisation, benefit particularly from SaaS solutions because of their specific needs. These tools allow them to manage the growing complexity of their role more easily while offering significant productivity gains.
- Time savings and resource optimisation: by automating the time-consuming tasks linked to risk assessment and compliance report generation, SaaS solutions allow CISOs and DPOs to concentrate on high-value actions, such as anticipating cyber threats or drawing up broader security strategies.
- Greater visibility and real-time reporting: SaaS solutions offer dynamic dashboards that make it possible to track the state of compliance and risk management in real time. This makes communication with senior management and the other stakeholders easier, by providing clear and detailed reports.
- Assurance of compliance with international standards: for companies operating in several jurisdictions, ensuring compliance with the various regulations and standards (GDPR, NIS 2, ISO 27001) can be complex. SaaS solutions incorporate the requirements of the different regulations, guaranteeing continuous and simplified compliance.
- Adaptability and scalability: finally, a SaaS solution adapts easily to the growth and evolution of the company. Whether the organisation expands into new markets or new regulations are introduced, the SaaS tool makes it possible to evolve processes without needing to overhaul all of the internal systems.
Cybersecurity and compliance are two essential pillars for protecting companies against cyber threats and ensuring their long-term future. By adopting a proactive approach to risk management, implementing effective security controls and ensuring continuous compliance with regulations, organisations can reduce their exposure to cyberattacks while avoiding the sanctions linked to non-compliance.

SaaS tools play a crucial role by simplifying and automating these complex processes. They allow those responsible for security, such as CISOs and DPOs, to regain control of their cybersecurity, to centralise the actions to be carried out, and to collaborate more easily with the various internal and external stakeholders. Thanks to these solutions, they can concentrate on their real added value: anticipating threats and steering a solid and scalable cybersecurity strategy.


